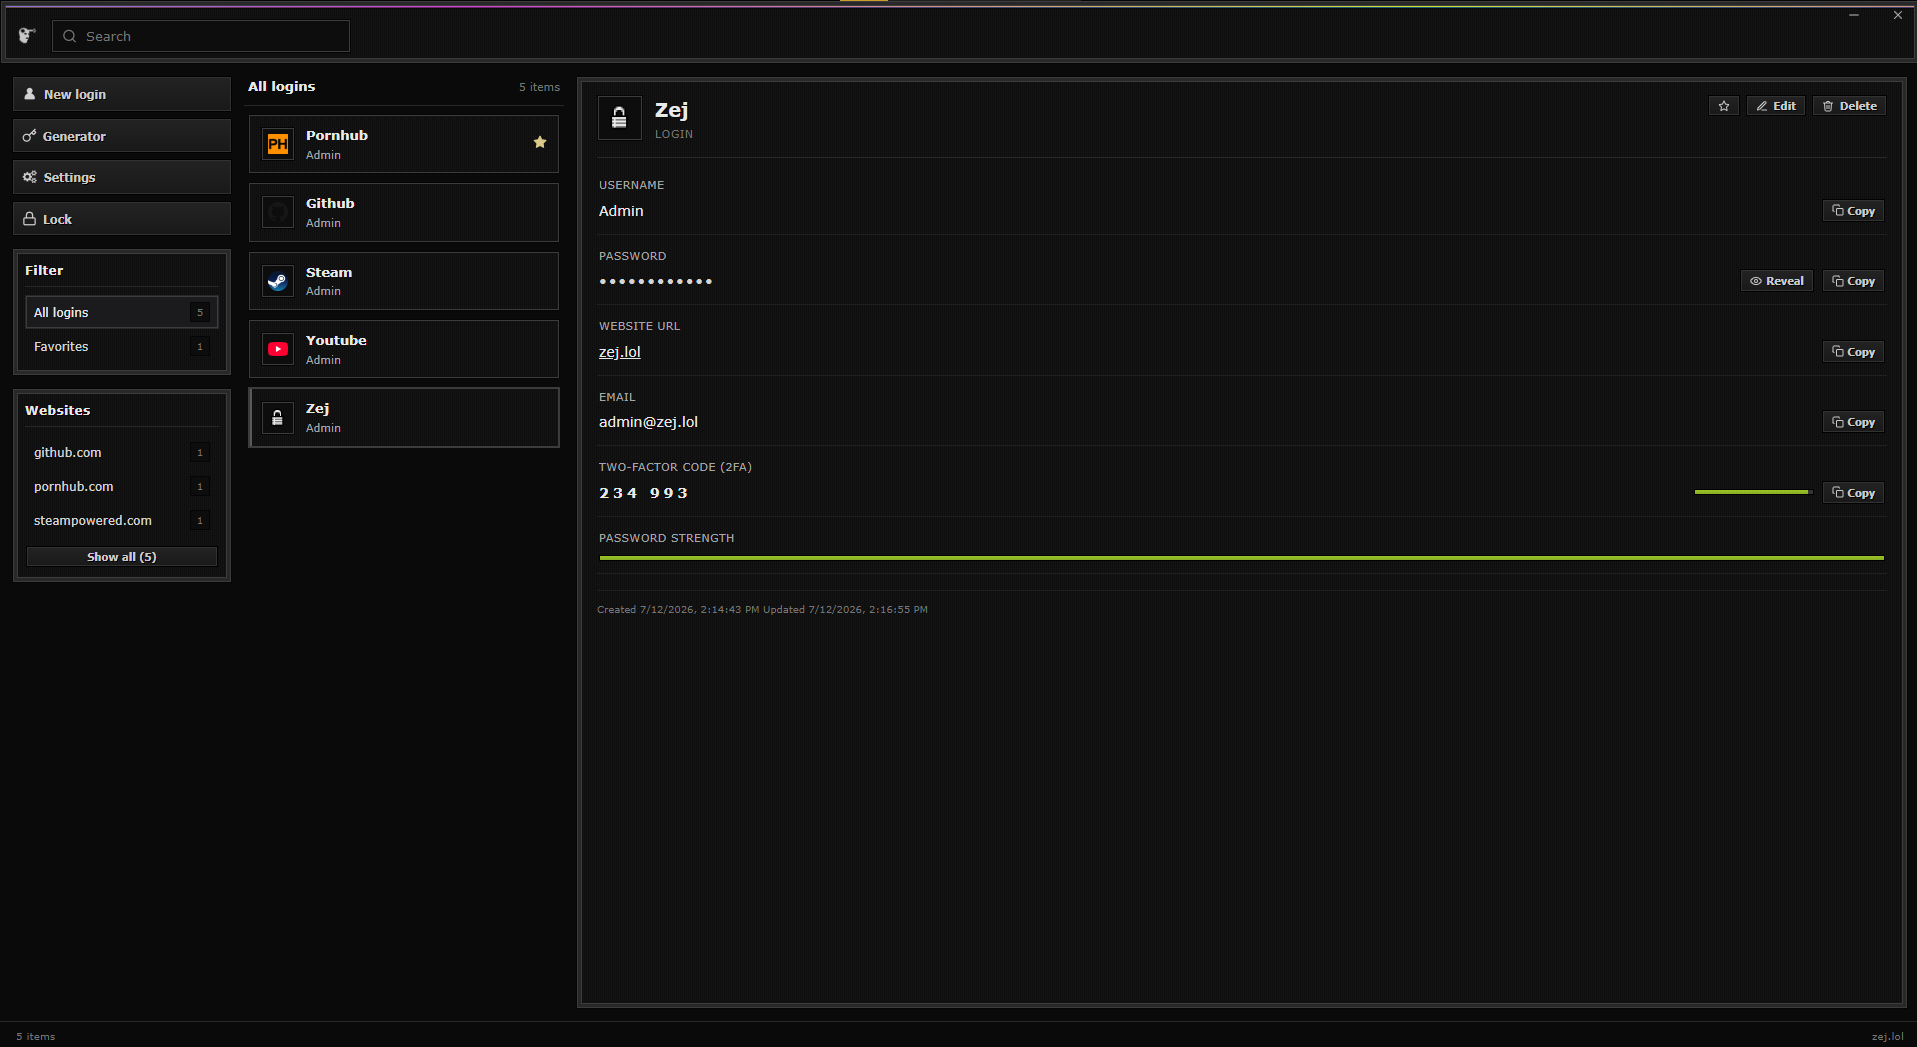
info-stealers copy your saved-password files in one pass and crack them later. i built skeet so that
doesn't get them anywhere.
two locks at rest
the vault is encrypted with AES-256-GCM (key from your master password via PBKDF2), then wrapped again in windows DPAPI. you'd have to break both to read a single login.
a copied file is dead
because of the DPAPI layer the vault won't decrypt on any other machine, even if they later crack or keylog your master password. that's the whole "steal now, crack later" plan gone.
nothing's stored in the browser
the extension holds no passwords. they only cross the local bridge when you ask for a fill, and only while the vault's unlocked. browser-password stealers find nothing.
loopback-only bridge
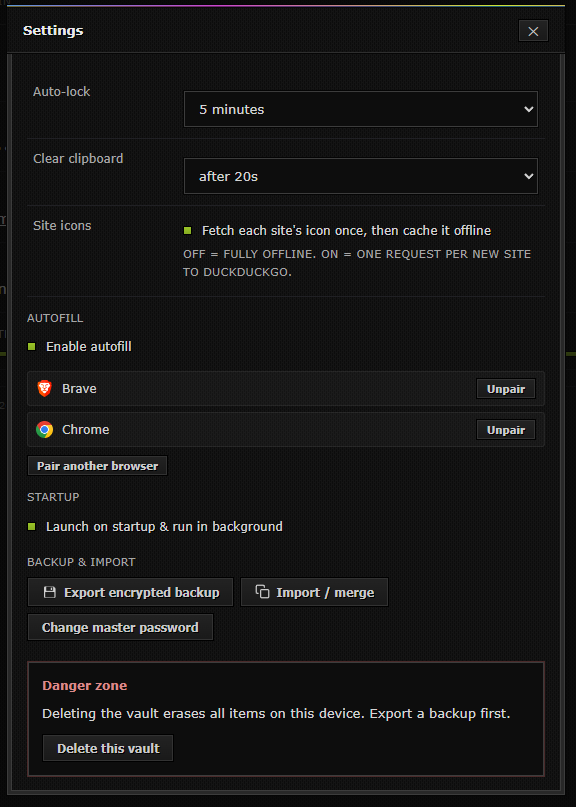
autofill runs on 127.0.0.1 behind a per-browser token. send that token to some server and it's useless. nothing off your machine can reach it.
no network, no account
your master password never leaves the pc and never hits disk. by default skeet makes no internet requests at all.
your call
site icons are opt-in (off = fully offline). auto-lock, clipboard timeout and startup are yours to set, and you can export an encrypted backup whenever.