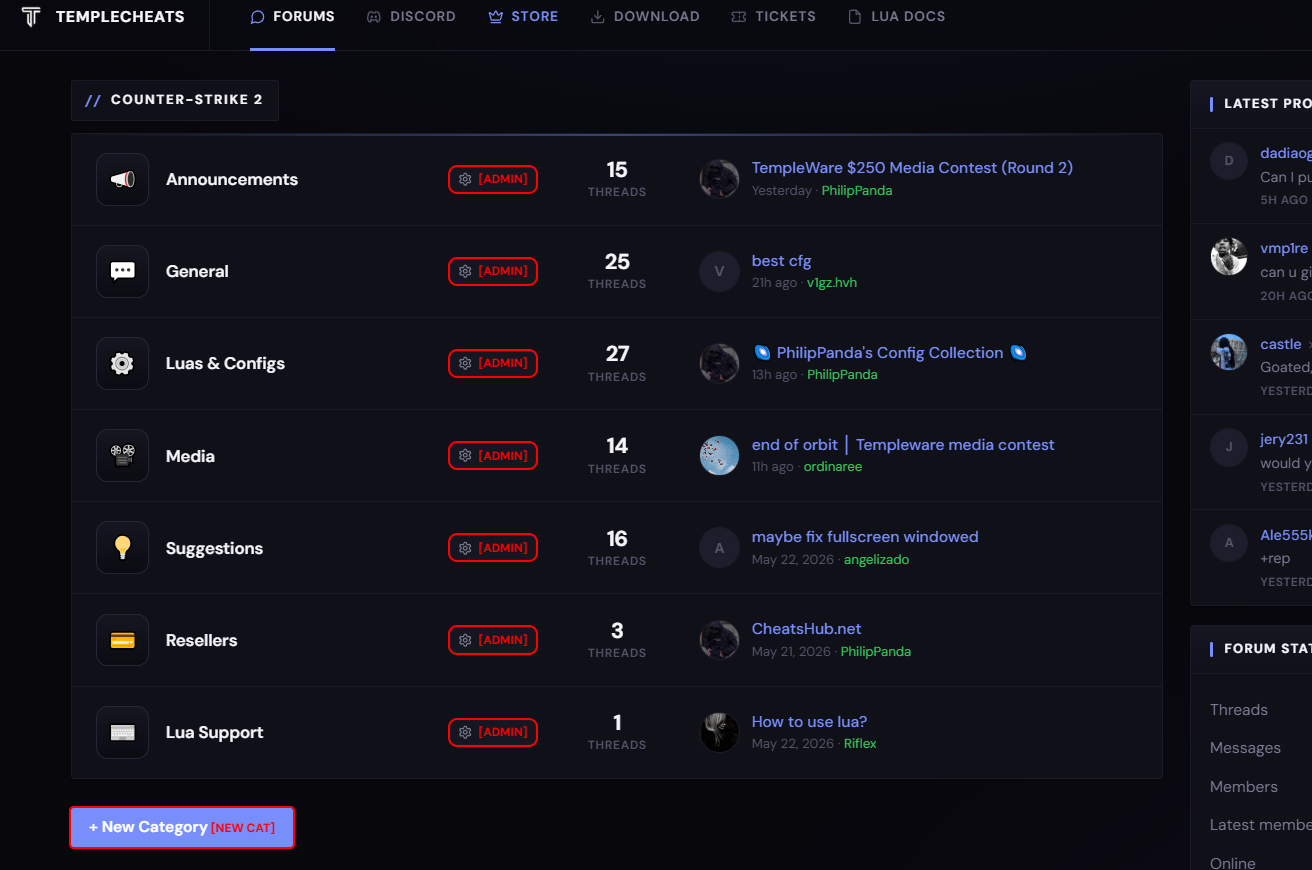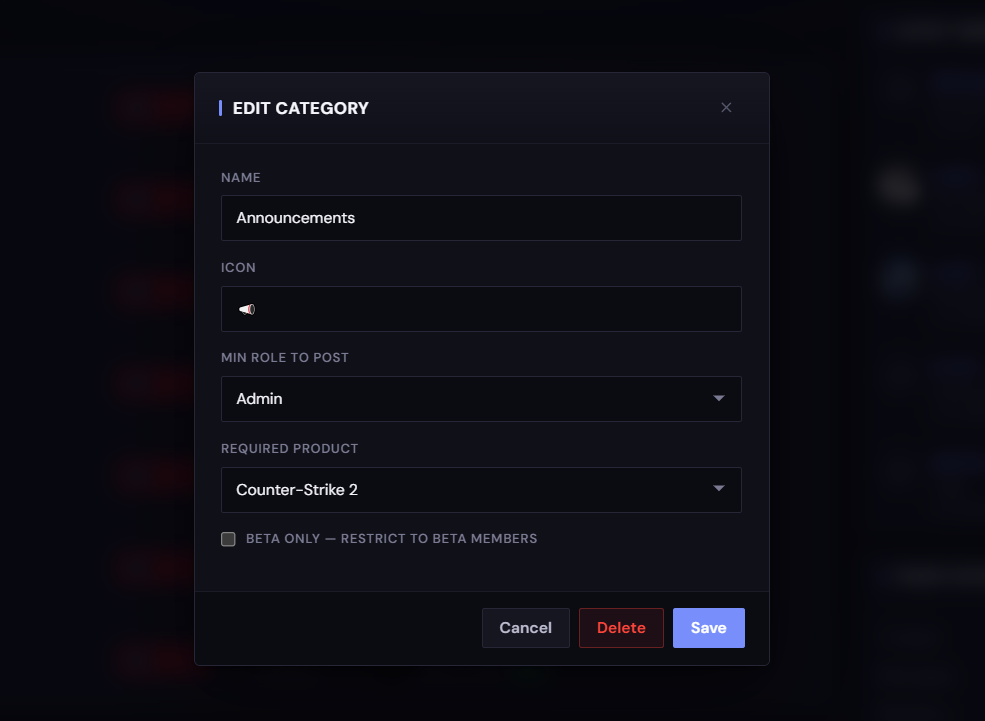
In this blog I am going to be talking about the process of pentesting templecheats.xyz
NOTE: This process was done via the approval of pentesting, given to me by the owner, this action shouldn't be done unless talked with the super admin of the website. If not talked through with and getting confirmation this can end in legal problems. I do not condone any malicious or illegal items on my site or actions, this goes for other blogs aswell. All of these issues have been fixed already by the superuser on the server.
Firstly we're going to be entering the website:
https://templecheats[.]xyz
What we see:
The login page; it's a private CS2 cheat forum, available for invited users to register.
We also see that the page is AI generated which mostly indicates low security on the server.
Next up we'll be going through the section of the website where different types of folders including the index.html are listed.
Looking through the index code, I notice 3 javascripts being included:
js/api.js
js/auth.js
js/shared.js
Looking through each and every one of them, I notice api.js keeps all their API endpoint links ready and steady to POST DELETE or GET.
This gives us information about the server infrastructure they are using, and leaves the frontpage open for vulnerabilities.
Auth.js sets up a JWT payload token for users who log on to the site. They recieve each item through their cache (a nex_token and a nex_u one). It also stores each rank inside of the localstorage IsAdmin IsUser IsMod IsPrem and so on and so forth.
As they keep this in their localstorage, you can easily intercept this and change your own rank, meaning gaining Admin on the website without even having to do the slightest thing.
Shared.js looks like it's just an embed helper for youtube videos or things of that sort.
We have analyzed the site throughly and are ready for pentesting. We open up burp suite, set up a Proxy, and start intercepting traffic. I won't be going into detail as much but you can learn how to use burp suite on https://portswigger.net/burp/documentation/desktop/getting-started
As we intercept traffic, we will be trying the localstorage hack to see if they have any protection when changing items inside of the clients storage.
...
Just like that theadmin panel has been accessed (Admin panel wont be shown for obvious reasons as it keeps user details, but a screenshot of the button will be linked)
By intercepting data inside of burpsuite we gained super user access on a members' account.
Thank you for reading.