my heaven on earth

blog about pentesting / reverse engineering
106 visitors

Website pentesting @ templecheats.xyz

In this blog I am going to be talking about the process of pentesting templecheats.xyz NOTE: This process was done via the approval of pentesting, given to me by the owner, this action shouldn't be done unless talked with the super admin of the website. If not talked through with and getting confirmation this can end in legal problems. I do not condone any malicious or illegal items on my site or actions, this goes for other blogs aswell. All of these issues have been fixed already by the superu…
Read more
Reversing A Custom Driver For The Valve Index (Specifically)

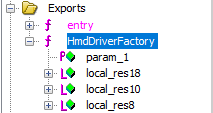
Symbol Tree Of Exports
Hello, this post is purely made out of boredom. Im typing this out while getting my tools ready to analyze this small DLL. This post describes quick reversing of a DLL in order to uncover its true identity ( If its malware or actual help in the community ) Tools used: Strings (https://learn.microsoft.com/en-us/sysinternals/downloads/strings), Ghidra (https://github.com/NationalSecurityAgency/ghidra) and x64dbg (https://x64dbg.com/) First I started to check the functions using a self made C++ to…
Read more

Reversing a Broken Rust Binary

Errors inside of an dissassembler
This post describes reverse engineering a Rust binary from the rev section of TBTL Capture The Flag 2024 (https://tbtl.ctfd.io/) . The challenge is named Safe Rust and provides a compiled Rust program. The challenge description indicates that the program “isn’t functioning properly”, and indeed, when we run it, we get the following message: thread 'main' has overflowed its stack fatal runtime error: stack overflow Interesting, let’s dig into the binary. The entry point, start, has a typical libc…
Read more